Choose the Randomness Contract Before a Number Picker Decides More Than a Draw
Separate casual random picks, reproducible simulations, and security-sensitive tokens before one random number workflow is trusted for the wrong job.
Open Random Number Generator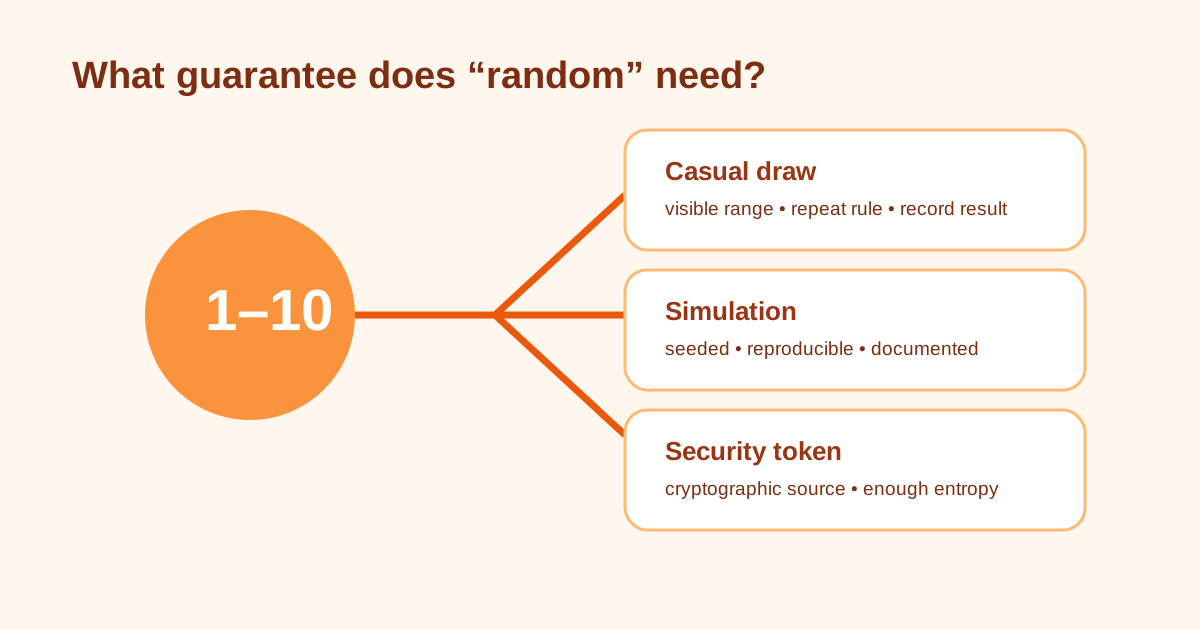
A number picker is asked to choose a workshop group, seed a test, and create a password reset code. All three outputs look random, but they have different requirements. Treating them as one problem makes the result difficult to audit, reproduce, or secure.
Name the contract before generating
- A casual draw needs a visible eligible range and a rule for repeats.
- A simulation may need a recorded seed so another person can reproduce it.
- A security token needs a cryptographically secure generator and enough entropy, not a convenient UI draw.
- A sample without replacement needs state that removes each selected item from the remaining pool.
The boundary problem that causes off-by-one bias
If the intended integers are 1 through 10, confirm that both endpoints are included. A formula designed for a half-open range can silently omit 10. Write the allowed set in plain language, generate several checks, and keep the range visible beside the result.
A fair and reviewable draw
- Freeze the eligible list or numeric range before the draw.
- Decide whether duplicate results are allowed.
- Use Random Number Generator for the declared range.
- Record the time, range, and result when the decision needs an audit trail.
- Use a dedicated cryptographic workflow for secrets, authentication codes, or keys.
FAQ
Are the minimum and maximum included?
Confirm the tool's displayed behavior and write the intended range explicitly. For a 1-to-10 draw, both 1 and 10 should be possible when the range is inclusive.
Can I reproduce the same random result later?
Only if the generator supports a seed and you record it. A casual browser draw is generally intended to produce a fresh result.
Should I use a random number picker for security tokens?
No unless it explicitly uses a cryptographically secure source and the token design has sufficient entropy. Use a purpose-built security mechanism.